When sensitive information surfaces where it shouldn't, EchoMark's investigation tools identify whose copy leaked, with a confidence score and chain-of-custody documentation, generally in minutes.


When sensitive information leaks, the clock starts immediately, but the evidence is rarely clean. It may be a screenshot, a photo of a screen taken on a personal phone, a printout, or a forwarded file with no record of how it got out. Traditional investigations rely on interviews, access logs, and educated guesses. Leak investigations generally stall in three places:
Every hour spent narrowing down suspects is an hour the information keeps circulating, and a wrong guess carries real cost to people and relationships.
EchoMark replaces guesswork with evidence by making every copy individually traceable before it's shared.
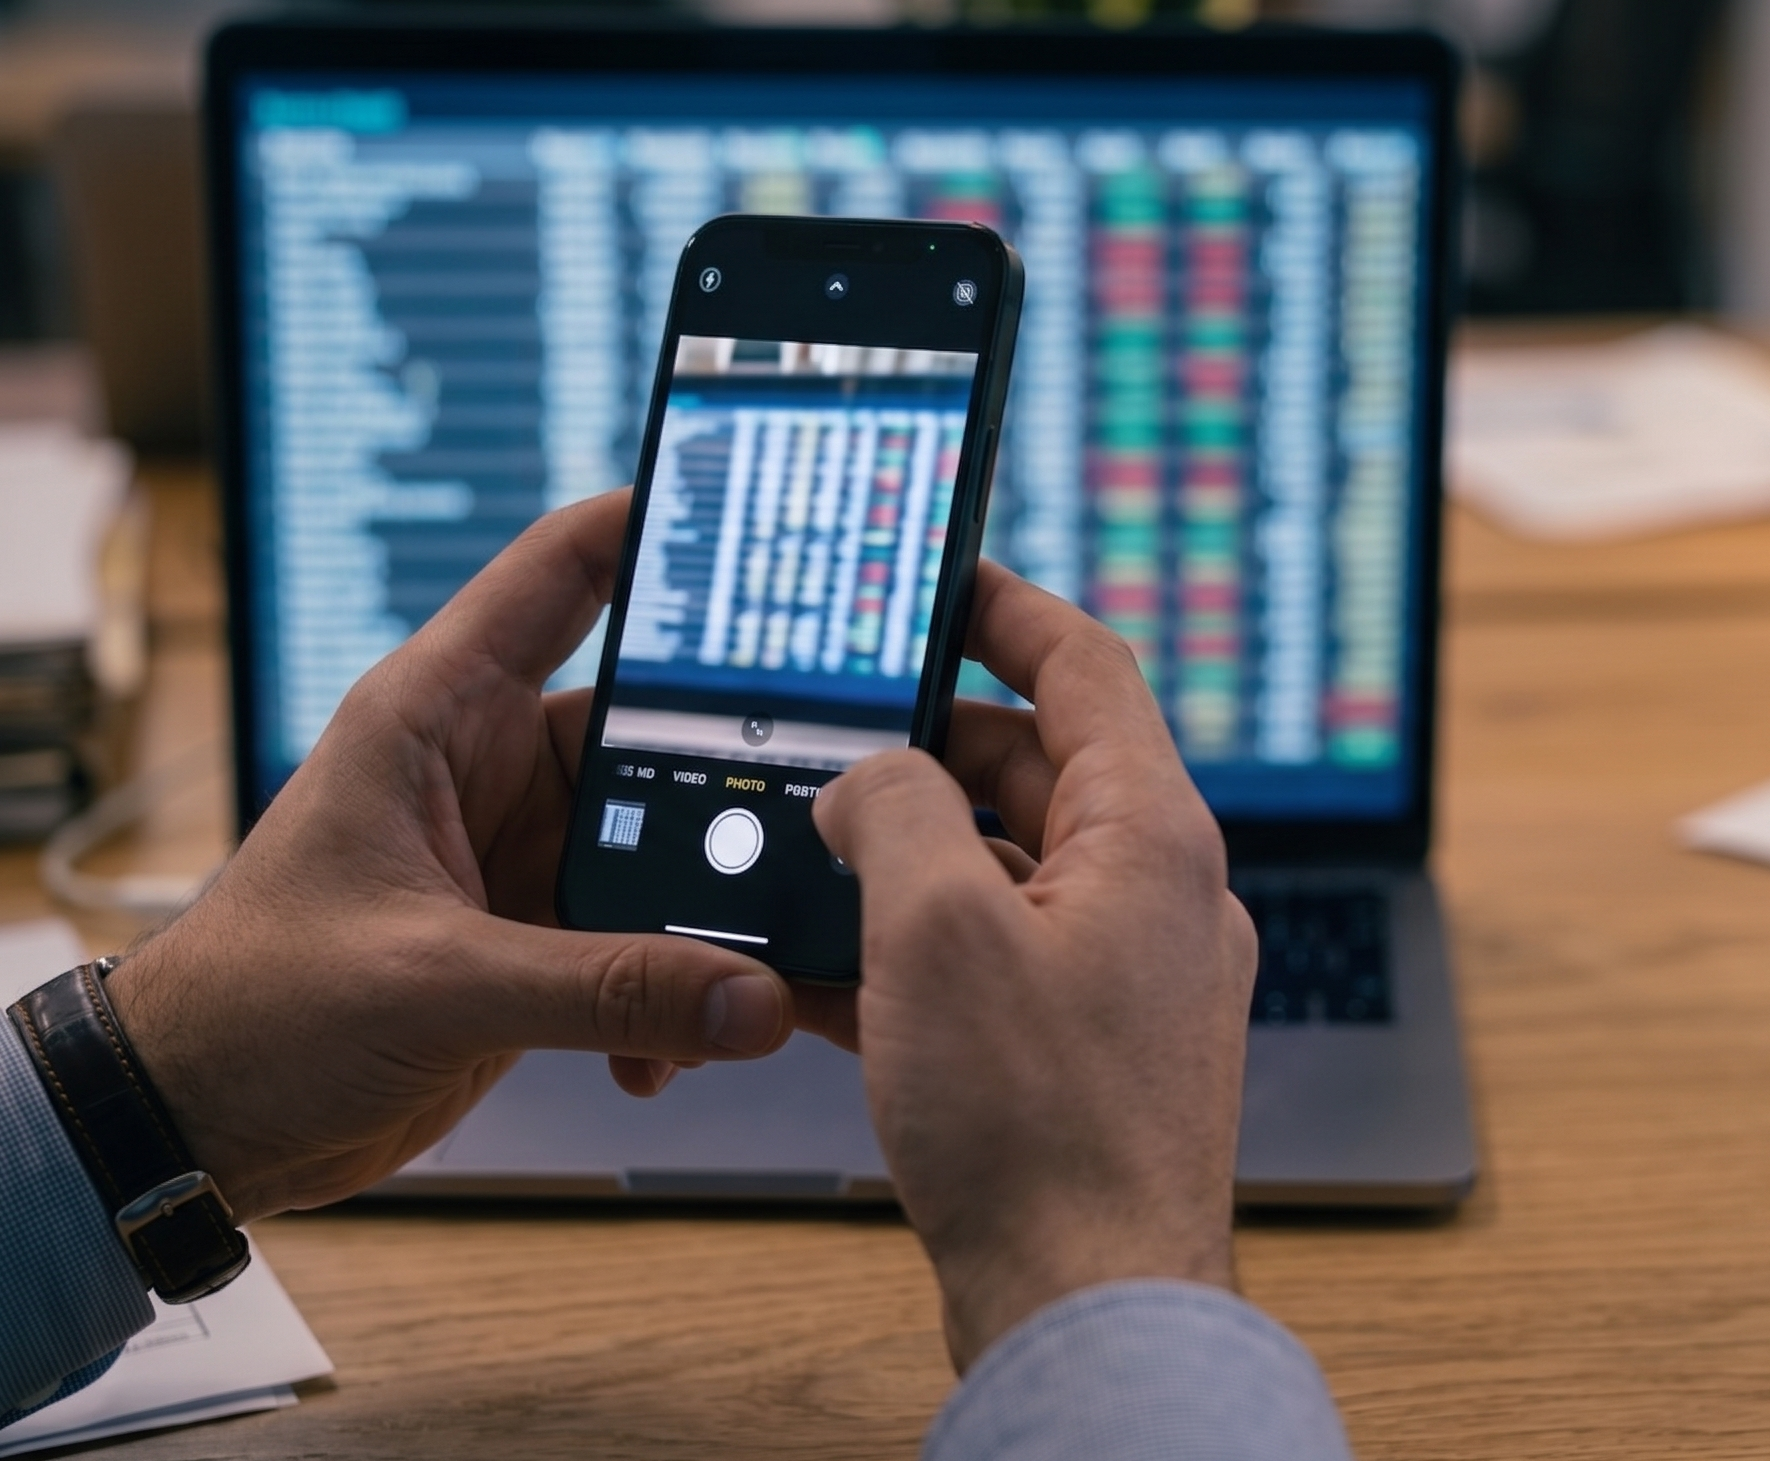

Using machine learning and computer vision, EchoMark determines the source of a leak. Invisible, individualized watermarks embedded in email, documents, screens, and content delivered through the API travel with the content, so even a photo or printout still identifies the copy it came from. These marks use steganographic techniques, meaning they're not metadata that can be stripped.
To investigate, upload the leaked artifact to EchoMark. Detectors identify whose copy was leaked, including a timestamp and confidence score, generally in minutes.
Every investigation produces a report that explains how EchoMark determined the source, along with transparent reporting on detector accuracy, so your security, legal, and HR teams can decide on next steps with confidence. Chain-of-custody documentation is available upon request. Schedule a personalized demo and we'll walk you through a real investigation, start to finish.
EchoMark investigations fit into the workflows you already have. The platform integrates with email services such as Microsoft Exchange and Google Workspace, complements security tools such as Microsoft Purview, supports single sign-on with your organizational identity, and can be deployed as multi-tenant SaaS, single-tenant, on-premises, or air-gapped.


EchoMark silently embeds invisible watermarks into every email, document, image, and screen.

You discover a sensitive screenshot, photo, printout, or file outside your organization.

Upload the leaked artifact to EchoMark's investigation tool to identify whose copy leaked, with a confidence score and chain of custody.
How does EchoMark find the source of a leak?
Upload the leaked artifact to EchoMark's investigation tool. The platform reads the invisible, individualized watermark embedded in that copy and matches it to the specific recipient it was created for, with a timestamp and confidence score, generally in minutes.
What types of leaks can EchoMark investigate?
EchoMark can investigate leaks of emails, PDFs and other documents, images, and on-screen content, including printouts and photos or screenshots taken on a personal device. Text watermarks are designed to survive re-typing, so even a rewritten version can still be traced.
What if the leak is a photo of a screen or a printout?
That's exactly the case EchoMark is built for. The watermark is embedded in the content itself rather than in metadata, so it's designed to persist through phone photos, screenshots, printing, and photocopying, closing the analog gap that logs and network tools can't see.
What do I need to start a leak investigation?
The leaked artifact is the starting point. Upload it to EchoMark's leak analysis tool; EchoMark's detectors handle the analysis and deliver a full report.
What does a leak investigation report include?
Reports explain how EchoMark determined the source and include a confidence score for the match, along with transparent reporting on detector accuracy. Chain-of-custody documentation is available upon request.
Can the evidence be used in legal or HR proceedings?
The investigation report and chain-of-custody documentation give your legal, security, and HR teams documented evidence of whose copy leaked. How to use that evidence is a decision for your counsel and your organization's policies.
How is this different from DLP, SIEM, or log analysis?
DLP, SIEM, and logs record activity inside your systems, but none of them can tell you who leaked a specific copy once it's outside those controls, such as a photo taken with a personal phone. EchoMark complements them by making every copy individually traceable, so the leaked artifact itself identifies its source.
What should we do immediately after discovering a leak?
Preserve the leaked artifact exactly as it was found — don't crop, edit, or re-save it — then upload it to EchoMark. The platform identifies which recipient's copy was leaked and provides chain-of-custody documentation your legal or security team can use to decide how to respond.
See how EchoMark can be seamlessly integrated with your Microsoft Exchange or Google Workspace to automatically embed invisible watermarks in messages, images, and documents.


