The full EchoMark platform is now available on Europe-based infrastructure, with a new in-region partner to deliver and support it across Europe.
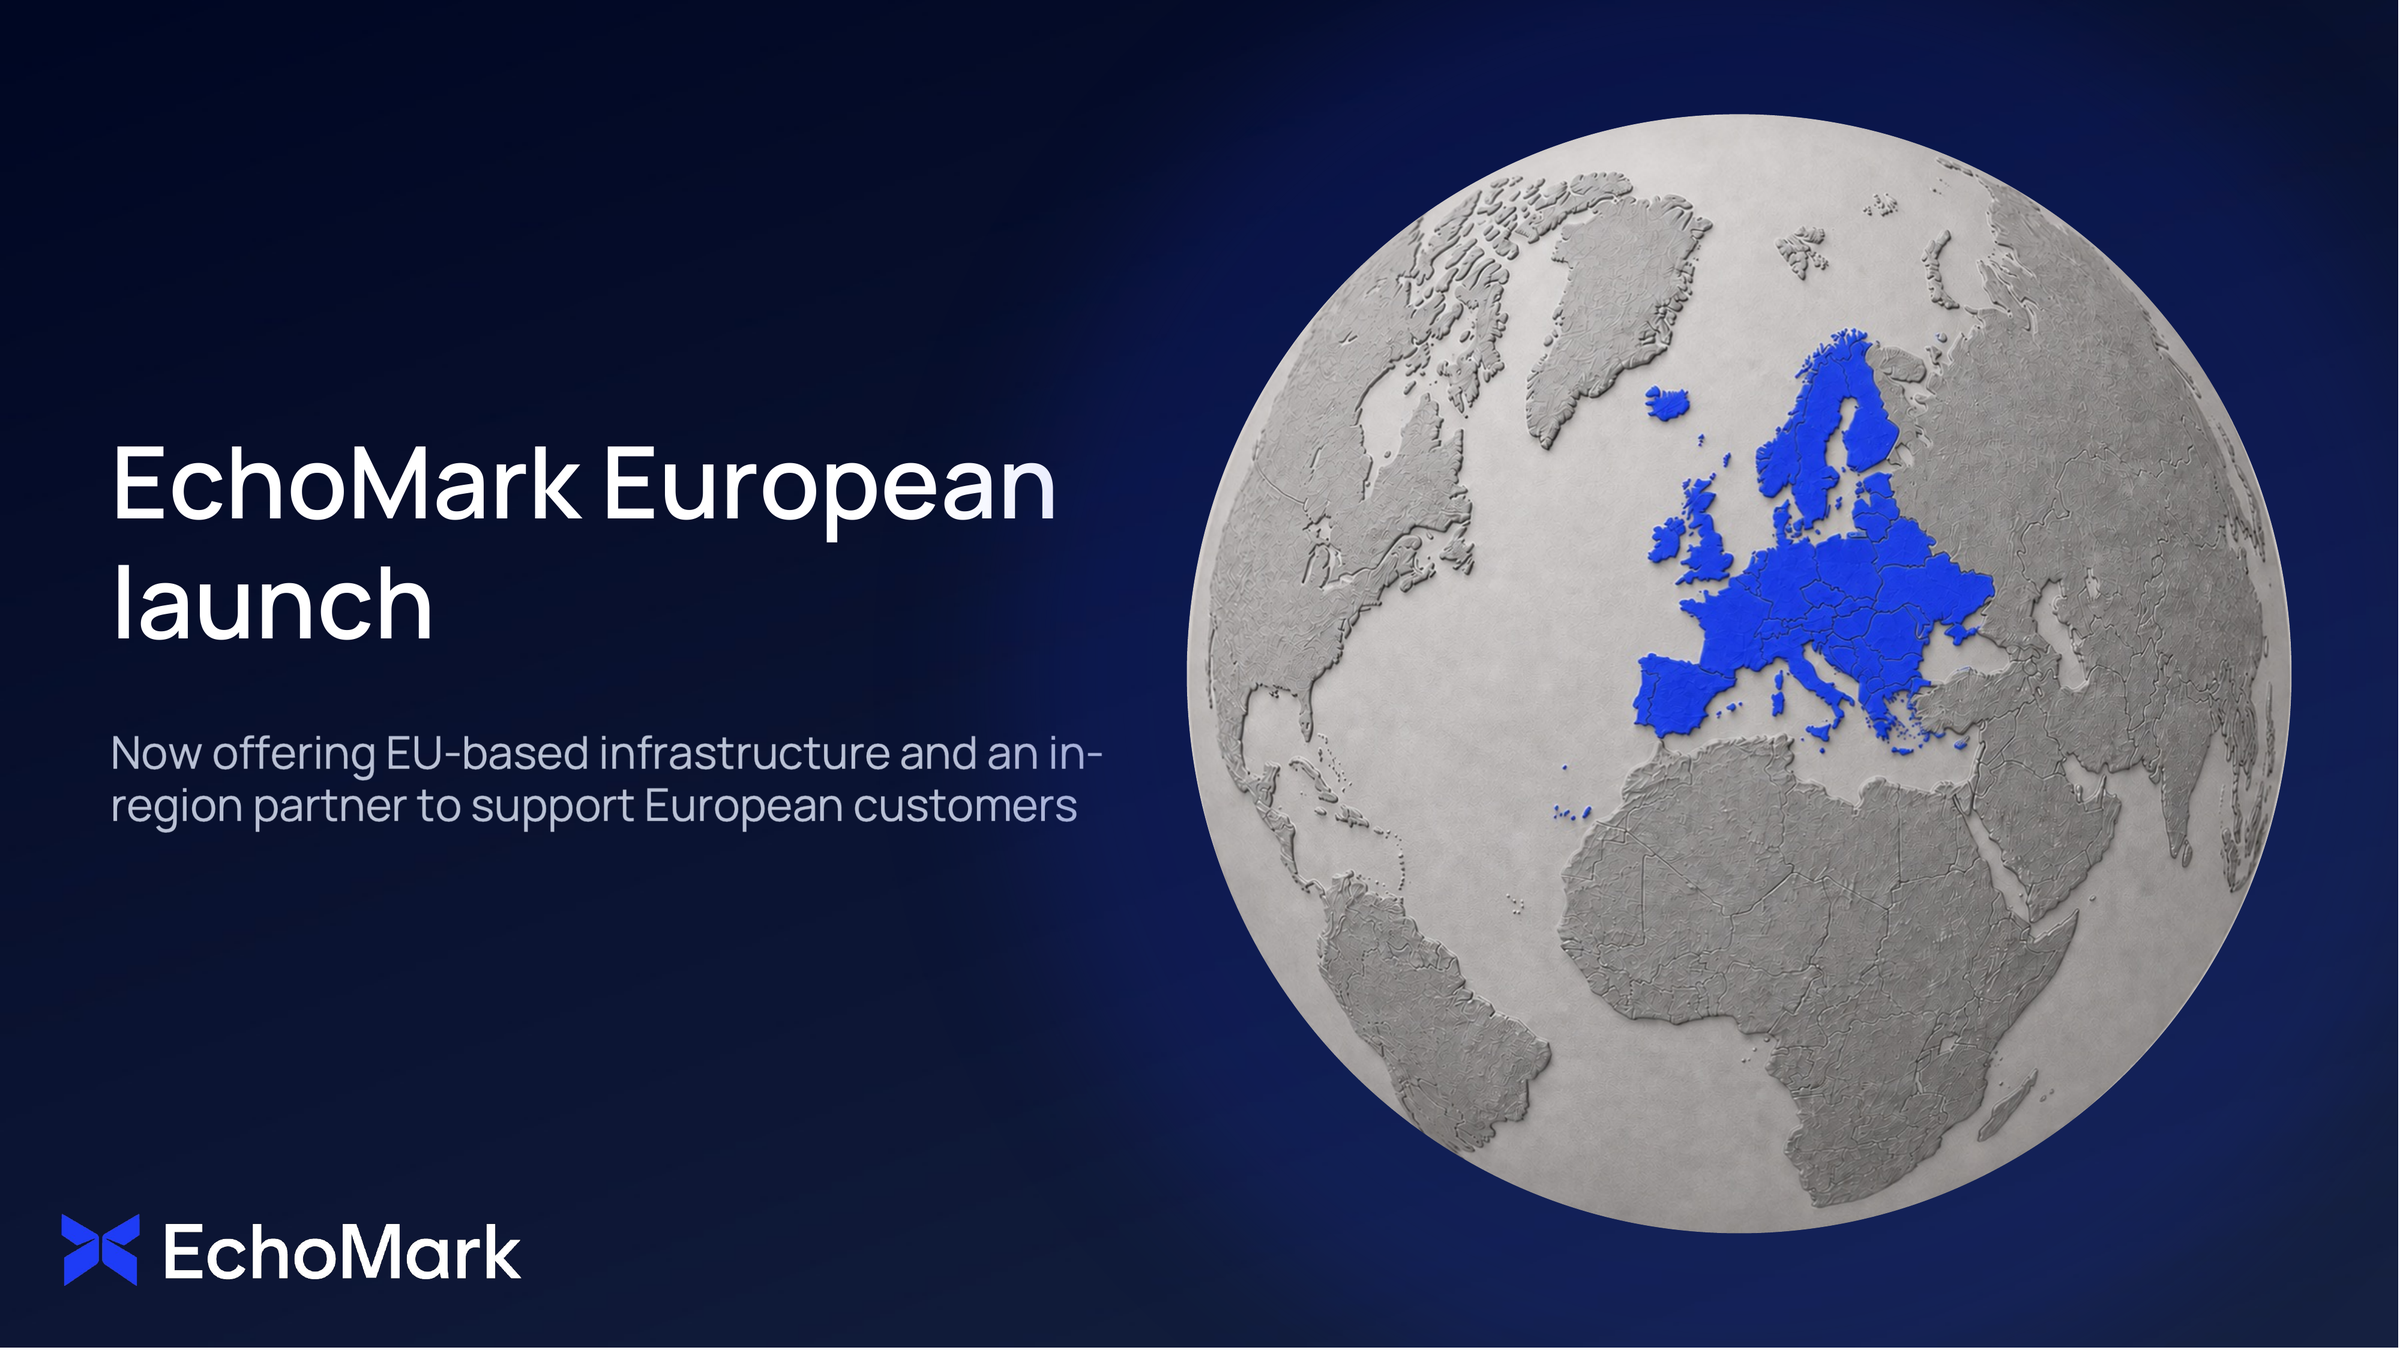
Week after week, sensitive internal information is reaching the press from across Europe. Automakers, EU institutions, and national governments have all had sensitive documents leak in recent weeks, and they are far from alone. Leaks don't stop at borders, and European organizations operate under some of the most demanding data compliance requirements in the world. When sensitive information escapes, boards and regulators expect a documented answer with tools that keep data and evidence in region.
That's the standard our new European operations are built to meet. The complete EchoMark platform is now available with European Union data residency, so customers can run watermarking, administration, and leak investigations entirely on EU-based infrastructure, from the moment content is marked to the final forensic report. We're also partnering with Nomios to deliver, deploy, and support EchoMark across the region, and expanding our work with insider risk organizations in the region.
European customers can now elect to run every part of EchoMark within the EU, including EchoMark Email, EchoMark File Share, EchoMark Screen, the EchoMark API, and the EchoMark app. Content is marked, managed, and investigated on EU-based infrastructure, with the same forensic capability customers rely on everywhere else.
Data residency isn't only a concern for highly regulated industries. GDPR applies to organizations in every sector that process the personal data of people in the EU, and requires them to know and document where that data is processed, who can access it, and on what basis it leaves the EU. With EU data residency, EchoMark customers can keep watermarking and investigation data in region, simplifying those answers with no reduction in functionality or sophistication.
Some sectors face additional frameworks on top of GDPR. Financial entities subject to the Digital Operational Resilience Act (DORA), and organizations covered by national laws implementing the NIS2 Directive, can now trace the source of a leak, whether deal terms, board materials, or sensitive operational documents, while keeping the investigation and its evidence on EU infrastructure.
Gaming and entertainment studios, often under contractual and reputational pressure to keep data in region, can deploy the full platform too, using EchoMark File Share for scripts and concept art shared externally and EchoMark Screen for pre-release game and film footage.
Technology alone isn't enough. European organizations expect the tools they adopt to be deployed and supported by providers who understand their market, which is why we've partnered with Nomios.
Nomios is a leading European cybersecurity services company, with a portfolio spanning consulting, integration, support, and managed services, including its own security operations centers. Its customers include enterprises and public sector bodies in some of the industries most exposed to insider risk. Under the partnership, Nomios will deliver, deploy, and support EchoMark for its European customers, building forensic watermarking and leak attribution into the security programs it already runs for them.
We're also contributing to the research and best practices that European organizations will rely on. EchoMark has joined the Insider Risk Practitioner Alliance (IRPA) as a Secretariat Tier 2 Partner, and Troy Batterberry, CEO and Co-founder of EchoMark, has joined IRPA's Industry Advisory Council. EchoMark is also a Gold sponsor of the UK Insider Risk Management Collaboration Centre and the Nordic Insider Risk Management Centre of Excellence Summits.
European data residency builds on the deployment flexibility we've spent years developing for our most demanding customers. EchoMark already runs in multi-tenant and single-tenant SaaS, as well as government special cloud and air-gapped environments. EU-based infrastructure is a natural extension of that approach, and it means European customers get the same platform, running where their data needs to stay.
When a leak surfaces, the question is always the same: whose copy was it? European organizations can now get that answer, often in minutes, with forensic evidence that is stored and processed in the EU.
Schedule a demo to see how EchoMark can protect your organization's most sensitive information, wherever it operates.
-----
1. Can EchoMark keep our data within the European Union?
Yes. European customers can elect to run the full EchoMark platform on EU-based infrastructure, including EchoMark Email, EchoMark File Share, EchoMark Screen, the EchoMark API, and the EchoMark app. Watermarking, administration, and leak investigations all take place on EU infrastructure.
2. Is the EU-hosted platform different from EchoMark elsewhere?
No. European customers get the same platform and the same forensic capabilities as customers anywhere else. EU-based infrastructure joins the deployment options EchoMark already offers, which include multi-tenant and single-tenant SaaS, government special cloud, and air-gapped environments.
3. How does EchoMark identify the source of a leak?
EchoMark uses steganographic techniques to embed an invisible, individualized watermark into every copy of an email, document, shared file, or screen, so each recipient receives a copy that is uniquely theirs. When information leaks, investigators upload the leaked artifact to EchoMark, which decodes the watermark and identifies which copy was the source, often in minutes, with forensic evidence and chain-of-custody documentation.
4. Does the watermark survive photos, screenshots, and printouts?
Yes. Because the watermark is embedded in the content itself, rather than in file metadata or on a device, it persists when information is photographed on a phone, captured as a screenshot, printed, or copied as email text. Conventional tools like DLP and access logs were not designed to trace these types of leak paths.
-----
EchoMark embeds invisible, individualized watermarks into emails, documents, images, and screens. When sensitive information leaks, EchoMark identifies whose copy was leaked, often in minutes, with forensic evidence.